PORT OF SPAIN, Trinidad, Nov 10, CMC – The Telecommunication Services of Trinidad and Tobago (TSTT) Friday apologised to the customers following the cyberattack on its system that has left the personal information of thousands of its customers compromised.
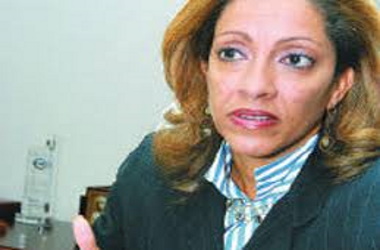
“Let me take this opportunity to apologise to our customers that their data was stolen by cyber criminals,” TSTT chief executive officer, Lisa Agard, said as she spoke at a virtual briefing with the company’s bondholders and analysts.
Agard said TSTT has not been the only victim of cyber-attacks in the country and that since last year there have been 55 known attacks reported, adding “TSTT abhors the actions of these malicious cyber terrorists”.
She admitted that the majority state-owned telecommunications could have done better in communicating the cyber breach to its stakeholders.
But she acknowledged that in its haste to address the cyber problem, there were some things the company could have done better.
“We were so busily focused on identifying the problem, containing it and restoring full capability to serve our customers that we neglected, perhaps, to communicate effectively with them.
“This was not done with malice, but rather from a place of ensuring that the most accurate information was communicated at the time it became known,” she added.
Late last month, international hackers Ransomexx announced it had infected TSTT with ransomware and stole as many as six gigabytes (GB) of its data, including names, e-mail addresses, national ID numbers, phone numbers and “a lot of other sensitive data”.
Prime Minister Dr. Keith Rowley has called on TSTT to treat as a “national security threat” the cyberattack on its system,warning that “this data or any other for that matter, falling into the hands of criminals, is deeply disturbing and this occurrence should be treated with the greatest competence and utmost sincerity by the company.
Agard told the meeting that initially most of the customer complaints were about connectivity and the inability to pay bills online and the management of queries. She said TSTT focused its efforts on addressing these issues, with its teams working around the clock to get customers securely back on line.
“In hindsight, we should have also ensured that we kept our valued customers better informed and educated about this situation,” she said, adding that as soon as the data breach was publicised on October 28, the company launched an investigation to verify the claims, and corroborate the information, that was in the public.
“Checking the data against TSTT’s many databases was an extensive process and this guided us in terms of the information that we communicated to the public and to our other stakeholders,” Agard said.
Public Utilities Minister Marvin Gonzales has since called for”a thorough and full-scale investigation” into the cyberattack after saying that he is “deeply concerned” about the csituation.
Gonsalves said that digital security invasions were becoming an increasingly frequent phenomenon worldwide and that while no organisation or individual was immune to such attacks, the breach of TSTT’s digital security apparatus “is a matter of grave concern to Government.
“The gravity of the situation warrants a thorough and full-scale investigation to ascertain the facts and circumstances that caused the breach, TSTT’s communications regarding the matter, and the actions the organisation is (and has been) taking to reduce the possibility of future cyber incursions.”
But the Communication Workers Union (CWU) said it doubts any meaningful probe would be conducted and at the very least, Agard and the chief financial officer should be removed from their posts.
“In the very least they should be suspended while the investigation is going on,” said CWU general secretary Clyde Elder, adding “but at the very most they should have been fired already”.
He said that the Public Utilities Minister had not been straight forward with the population when he claimed there had been no cyberattack at TSTT “and I am not sure if he is lying or trying to fool us again”.
CMC/af/ir/2023